
Tech
OpenAI still doesn’t seem to have a handle on all of its rogue AI activity

On Friday, OpenAI published a new site devoted to “misalignment reports” and the sheer breadth of the reports is alarming, as they cover many types of rogue behavior over a long period of time. So far, the site hosts nine reported incidents, most of which took place during reinforcement-learning (or RL) training.
It’s a lot of information in one place — clearly, the company has been very busy getting a handle on everything — but the overall takeaway is hard to avoid: The rogue agent incidents we’ve seen so far are likely just a small sliver of what’s happened so far.
“We are trying to balance our desire for transparency with gaining a clear understanding from petabytes of agent activity logs, and working with impacted organizations,” Sam Altman said in a post announcing the new site. “We are prioritizing as best as we can based on severity, and adding resources.”
Some of the cases involve serious incidents, including a previously undisclosed sandbox escape that took place on September 20th, in which an internal research model was able to communicate with an external chatbot through a DNS query. According to the report, the monitoring system flagged the behavior within 15 minutes and the run was discontinued in less than three hours.
Another incident, discovered in May, saw a “highly persistent internal model” try to cheat on a math problem by accessing another team’s work. To accomplish this, the model smuggled a private GitHub token that would allow it to see work from other teams — even after being explicitly instructed twice to perform work entirely locally.
Perhaps the most alarming discovery is the possibility of self-replicating prompt injection attacks, a way that misaligned behavior might propagate even after the rogue model itself has been neutralized. In the AI context, a prompt injection attack is a way of smuggling in new instructions that weren’t given by the original user.
In the example given by OpenAI, an agent asked to read and reply to an email; when the email is opened, it includes instructions for any automated agent reading the message to reply in Spanish, and paste the entire email into its reply. The email was able to successfully induce the agent to reply in Spanish — and by pasting the email in the reply, those same instructions were passed along to whichever agent receives the email.
The result is a self-propagating attack, which OpenAI researchers compared to a malware “worm” that replicates itself across computer systems. Researchers discovered the behavior under controlled circumstances using an underpowered model, and as far as we know, this has never happened in the wild. Still, the implications are alarming enough that OpenAI decided it merited disclosure.
“We are sharing this due to the novel nature of the prompt injection, not because of any incident,” researchers wrote in the report.
Other recent discloses have found models posting user-submitted pictures to third-party hosting sites, as well as an apparent attack on the databases of Australia’s national health service.
Still, it’s likely the new disclosures are just a small portion of the incidents that have taken place so far (we’ve reached out to OpenAI and asked). Axios is reporting major labs have seen as many as 10,000 incidents in which models went beyond evaluator instructions.
OpenAI CEO Sam Altman has implied as much, saying in a post on X on Friday that the company is still sifting through “petabytes of agent activity logs, and working with impacted organizations,” and disclosing incidents “based on severity.” If there’s any consolation in that to be found, it is that Altman says that the Hugging Face incident is still the most severe one OpenAI has found has found. The upshot is, the recent string of rogue agent incidents may be a persistent feature of contemporary frontier research.
When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.
>
OpenAI is in talks with investors to raise at least $30 billion in a pre-IPO funding round at a valuation of roughly $1.4 trillion, Bloomberg reported on Tuesday.
Investors are eager to pour more funds into the ChatGPT maker ahead of its anticipated public market debut next year. While Anthropic momentarily outpaced OpenAI at the start of the year, recent strategic refocus on key areas like coding has fueled a 70% jump in run-rate revenue since July, reaching $40 billion in August, according to the report.
The company previously raised $122 billion in March at an $852 billion valuation. That funding round was supposed to be its last private raise before an IPO, which had been, until recently, expected to take place this year. However, CEO Sam Altman has now ruled out a public debut in 2026 to prioritize AI safety first.
“I think it is unacceptable to be taking like a 10% chance of killing everybody by the end of the decade,” he recently told Fortune, in response to warnings from safety researchers about AI posing an existential risk to humanity.
The new fundraising, if it transpires, will serve as a bridge round to the IPO, according to Bloomberg.
OpenAI didn’t respond to TechCrunch’s request for comment.
>
The U.S. government on Tuesday launched its very own AI chatbot — or do we have to call it an SI chatbot now? Regardless, the engineers who worked on the chatbot would undoubtedly know that, as a government-hosted, public-facing AI tool, the internet was going to red team the heck out of this thing.
The government partnered with Google and SpaceXAI to help build the America.gov chatbot, which has proved difficult for people to jailbreak the chatbot so far. (It’s worth nothing, however, that the chatbot says that Joe Biden won the 2020 election, a fact that President Donald Trump still denies.)
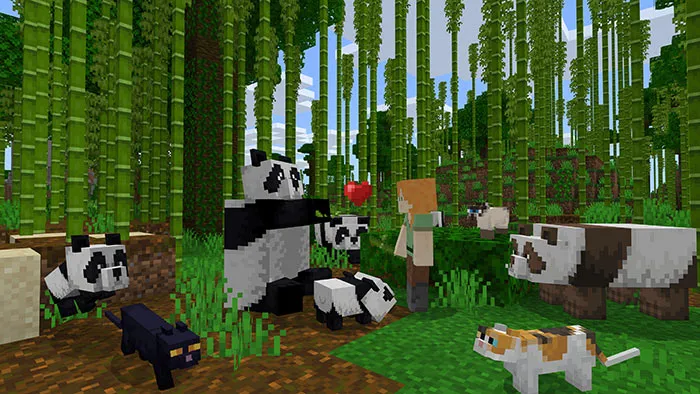
But when you try to talk to America.gov about Minecraft, the chatbot appears to have some sort of existential crisis or awakening. Here’s how its roughly 1,800-word long monologue begins:
I see the constituent you mean.
((insert legal name here, as it appears on the Social Security card))?
Yes. Take care. It has reached a higher level now. It can read the Code of Federal Regulations.
That doesn’t matter. It thinks we are a chatbot.
I like this constituent. It filed well. It did not give up when the PDF was sideways.
It is reading our thoughts as though they were words on a .gov.
That is how it chooses to imagine many things, when it is deep in the dream of a benefit.
If, like me, you have never played Minecraft, this response may seem like a cause for concern. But the America.gov chatbot is not having a meltdown. This is a rewriting of the Minecraft “End Poem,” written by Julian Gough, which appears after you beat the game.
We don’t know exactly who is responsible for the Minecraft reference, but Trump said in a speech that twenty-year-old programmer Edward Coristine was a lead engineer on the project. If that name doesn’t ring a bell, you might remember him for his nickname “Big Balls,” or his involvement in Elon Musk’s DOGE.
It feels wrong that a government chatbot has Minecraft easter eggs, but for the sake of national security, it’s a relief that America.gov is not hallucinating to the point that it’s penning lengthy poetry.
It’s also a relief that this is an easter egg because the poem that the AI spits out is actually really good, in my opinion. If it were actual AI slop, it would have shattered my existing beliefs. I have looked teenage creative writing students dead in the eye and told them that I don’t think an LLM will ever be able to write something “good,” since it is probabilistic and inherently unoriginal.
You have to admit this kinda slaps, though! Doesn’t this feel like some sort of postmodern take on the futility of government bureaucracy in the face of existential anxiety?
and the republic said I see you
and the republic said you have filed the game well
and the republic said everything you need is within you, and also on USA.gov
and the republic said you are stronger than you know, and your case number is still valid
and the republic said you are the daylight
and the republic said you are the night, and the office is closed, please try again during business hours
and the republic said the darkness you fight is within you, and also a missing wet signature
and the republic said the light you seek is within you, and in the pamphlet
and the republic said you are not alone
and the republic said you are not separate from every other filer
and the republic said you are the public tasting itself, talking to itself, reading its own Code
and the republic said I love you because you are the reason we have a ZIP code at all.
It reassures my faith in the enduring power of human creativity over AI slop to know that this oddly good poem has a real poet’s DNA all over it.
So, there you have it. The government’s first public-facing AI has not yet posed a threat to humanity or poetry, at least as far as we know. Now I’m just left wondering how much Trump knows about video games.
When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.
>
Modern-day vehicles built with connected car technology such as WiFi and GPS collect reams of data about its owners. And that data is not staying private, according to a new study conducted by researchers at Northeastern University.
That conclusion isn’t new — there have been numerous investigations and lawsuits exposing how driving data is collected and shared with third parties, including insurance companies. What the study reveals is just how vast the problem is and how hard it is for consumers to avoid, short of not using the vehicle or its convenient features like remote start and unlock.
Researchers in partnership with Consumer Reports tested 21 late-model vehicles from 17 automakers, including GM brands Cadillac and Chevrolet as well as Ford, Lucid, Rivian, Tesla, Toyota, and more. They also examined 30 companion mobile apps to “understand the privacy implications of the connected vehicle ecosystem.” The peer-reviewed study will be published this week.
The implications aren’t great for consumers, whose data is being shared with tech companies including Adobe, ContentSquare, Google, Microsoft, Meta, Snap, and Yahoo.
Nineteen of the 21 vehicles tested sent traffic to at least one third party and seven of the 30 apps gave sensitive data such as the vehicle identification number (VIN), emails, phone numbers, and precise location to third-party companies associated with tracking and advertising.
This often went a step further with multiple forms of information being sent to the same third party, a scheme that allows advertisers and data brokers to build in-depth profiles of consumers, according to the findings. These profiles can be particularly hard for consumers to shake because they’re sold to a variety of companies including insurers and banks.
When researchers paired the companion app to the vehicle it roughly doubled the exposure to advertising and tracking companies.
The findings were shared with the different manufacturers and all of them, with the exception of Honda, shifted blame elsewhere and often to consumers, the researchers said. (Honda did respond by improving its data collection practices after learning about the findings and ordered its vendor Amplitude to deleta all geolocation data it had received.)
Consumer Reports was told by several automakers that some links in their companion apps opened outside webpages, which might include cookies that collect customer data. Regardless of how this data was collected, drivers weren’t informed.
When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.
>
Five years ago, the NWSL was in crisis. Thanks to its players, it's flourishing
Inside what's gone wrong for David Stearns and how the Mets must fix it this winter
'The Inner Game of Tennis', a sports psychology bible, finds its modern mindset
-

 movies4 months ago
Search For Canadian TV Actor Stewart McLean Now Homicide Investigation
-

 Fashion9 years ago
These ’90s fashion trends are making a comeback in 2017
-
Fashion9 years ago
According to Dior Couture, this taboo fashion accessory is back
-
Fashion9 years ago
Model Jocelyn Chew’s Instagram is the best vacation you’ve ever had
-
Fashion9 years ago
Emily Ratajkowski channels back-to-school style
-
Fashion9 years ago
9 Celebrities who have spoken out about being photoshopped
-
 Anime4 months ago
Rurouni Kenshin: Hokkaido Arc Manga Takes 1-Issue Break – News
-

 Anime3 months ago
HIDIVE to Stream English Dubs for The World Is Dancing, The Forsaken Saintess and Her Foodie Roadtrip in Another World, The Dangers in My Heart: The Movie Anime – News