
Tech
AI evaluation startup Braintrust confirms breach, tells every customer to rotate sensitive keys

AI evaluation startup Braintrust has urged customers to revoke and replace their API keys after an earlier breach of customer secrets.
According to an email sent to customers Monday and seen by TechCrunch, the startup confirmed “unauthorized access” in one of its Amazon Web Services cloud accounts, which contained API keys used by customers for accessing cloud-based AI models.
“We’ve communicated with one impacted customer and to date have not found evidence of broader exposure,” read the email.
The email asked “every customer to rotate” any of the API keys that they store with Braintrust.
Braintrust disclosed the security incident on its website on Tuesday. “The incident has been contained, and in the meantime, we’ve locked down the compromised account, audited and restricted access across related systems, and rotated internal secrets.”
The company said the cause of the breach is under investigation.
Braintrust spokesperson Martin Bergman told TechCrunch that the company sent the email to customers “out of an abundance of caution,” and that it “confirmed a security incident, but there is no evidence of a breach at this time.”
Techcrunch event
San Francisco, CA
|
October 13-15, 2026
Braintrust provides a platform designed for companies to monitor AI models and products. Founder and CEO Ankur Goyal previously told TechCrunch that Braintrust is like an “operating system for engineers building AI software.” The startup raised $80 million in a Series B funding round in February, which valued the company at $800 million.
Jaime Blasco, the co-founder of cybersecurity startup Nudge Security who received a breach email alert from Braintrust, told TechCrunch that the incident could have “downstream implications for affected customers,” like AI companies that rely on Braintrust.
Contact Us
Do you have more information about this breach? Or other data breaches? From a non-work device, you can contact Lorenzo Franceschi-Bicchierai securely on Signal at +1 917 257 1382, or via Telegram and Keybase @lorenzofb, or email.
Hackers frequently target corporate accounts on cloud services or third-parties platforms as an effective way of stealing secrets, like API keys. Once hackers get their hands on API keys, they can log into the company or customers’ systems appearing as if they are legitimate users, without needing to break into the target company’s systems.
CircleCI, a company that provides development products for software engineers, was hit with a similar cloud data breach in 2023, and similarly asked its customers to rotate “any and all secrets” they stored with the company.
More recently, a EU cybersecurity agency said hackers were able to steal 92 gigabytes of data from a compromised Amazon Web Services (AWS) account used by the European Commission. The breach affected 29 other EU entities and the data of dozens of internal European Commission clients.
When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.
>
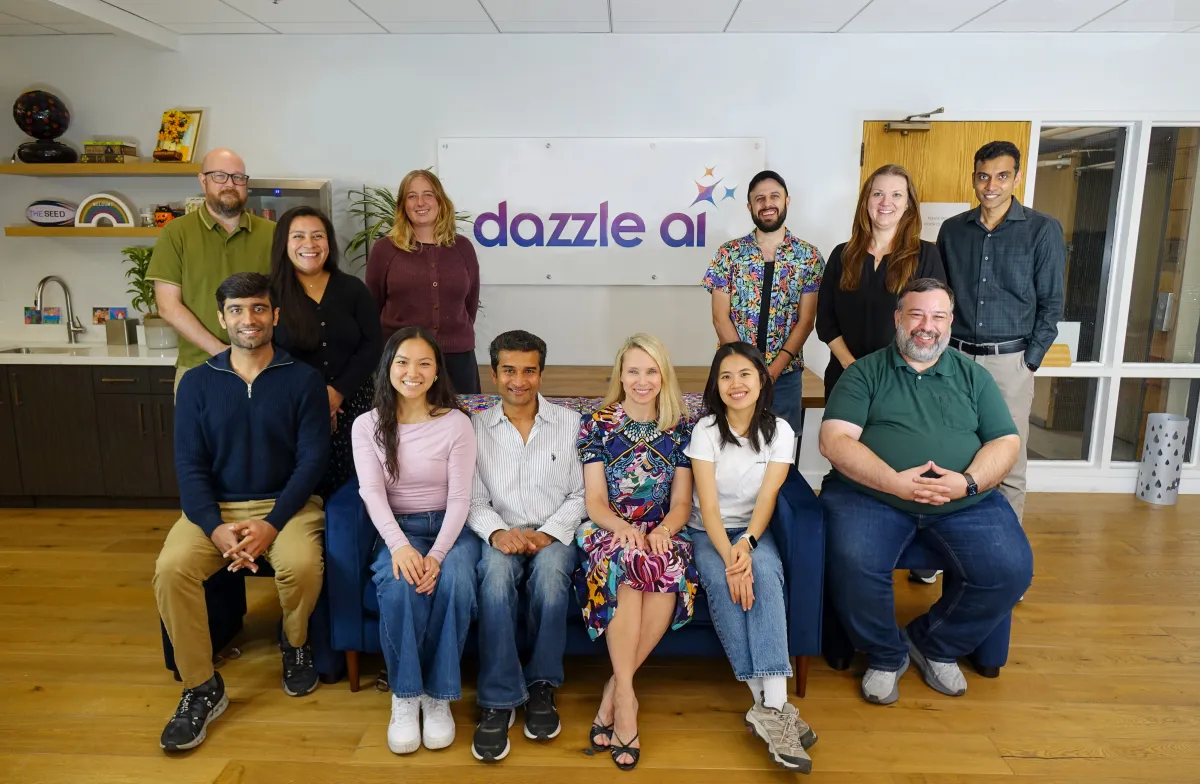
When former Yahoo CEO Marissa Mayer earlier this month told me she was finally ready to unveil Dazzle, the personal AI assistant that raised an $8 million seed round last December, I couldn’t help but wonder if she’s playing copycat to Meta’s Muse, Instinct, and the flood of similar tools that have flooded the market over the past month.
But when Mayer finally gave me a demo, Dazzle proved it’s taking a different approach. Instead of building context about you from text-heavy apps like email, calendars and shopping histories, Dazzle’s AI assistant gets all its context from a single source: your camera roll.
“I think that photos are an underappreciated source of information,” Mayer said. “You’ll be surprised what we can learn about you and how good a job we can do with your photos.”
Mayer argues that if a photo is worth a thousand words, your camera roll is worth millions. By analyzing all the photos stored on your phone, Dazzle claims to understand your hobbies, interests, food and style preferences, how you like to spend their time, and with whom.
“We understand whether or not you like to ski, where your most recent trip was, what types of things your kids are into,” Mayer said.
It’s no surprise that Mayer has built an assistant centered around photos. Her previous startup, Sunshine, launched an AI-powered photo-sharing tool called Shine in 2024. While that product was widely criticized for its outdated design, failed to attract widespread usage, and eventually shut down, Mayer says it nevertheless built “interesting IP.”
I was eager to try Dazzle, which users can use through its app or via text. Dazzle splits its functionality into two core experiences. For immediate tasks, it can scan recent photos to pull details — like populating your calendar from an event flyer, or finding a repair-person after spotting a broken garage door in your camera roll.
Second, it mines your photo library to come up with personalized ideas for everything from holiday vacations to birthday gifts.

Given that plenty of tools can parse pictures — like looking up where to buy a product, or searching information on an interesting art piece — I was far more curious to test what Dazzle could learn from my photo history.
For instance, Mayer uses Dazzle to brainstorm family outings. By scanning her photos, she says, the assistant deduced that her family loves escape rooms, and subsequently suggested multiple SF Bay Area locations she’d never heard of.
When I tested Dazzle with a request for vacation recommendations, it suggested several Mediterranean spots, likely picking up on my past trips to Spain and Greece. But it also threw in Sicily, which surprised me since I was there four years ago. After some more tinkering, I noticed it has blind spots — it failed to remember my daughter already knows how to roller skate when I asked if I should buy her a pair for her next birthday.
Despite the hiccups, though, I appreciated Dazzle’s ideas for activities, like suggesting a local pottery studio down the street, or a bioluminescent kayak tour in Tomales Bay.
I’m sure the product will improve with time, and while I’m undecided on whether I’ll keep using it, I like that its suggestions feel more personal than what you’d get from a generic AI assistant that only knows your calendar.
In the meantime, Mayer contends that given security concerns with products like Instinct and Muse, users may feel more comfortable handing over their photo libraries to an AI instead of granting it access to sensitive data like emails and messages.
She emphasized that Dazzle prioritizes privacy, and discards any personal information the AI flags as sensitive.
This flurry of new AI assistants is an exciting time for consumers. And while Dazzle isn’t as broadly useful as other offerings quite yet, it offers a glimpse of a future in which AI can do more than just execute tasks; it actually knows who you are.
When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.
>
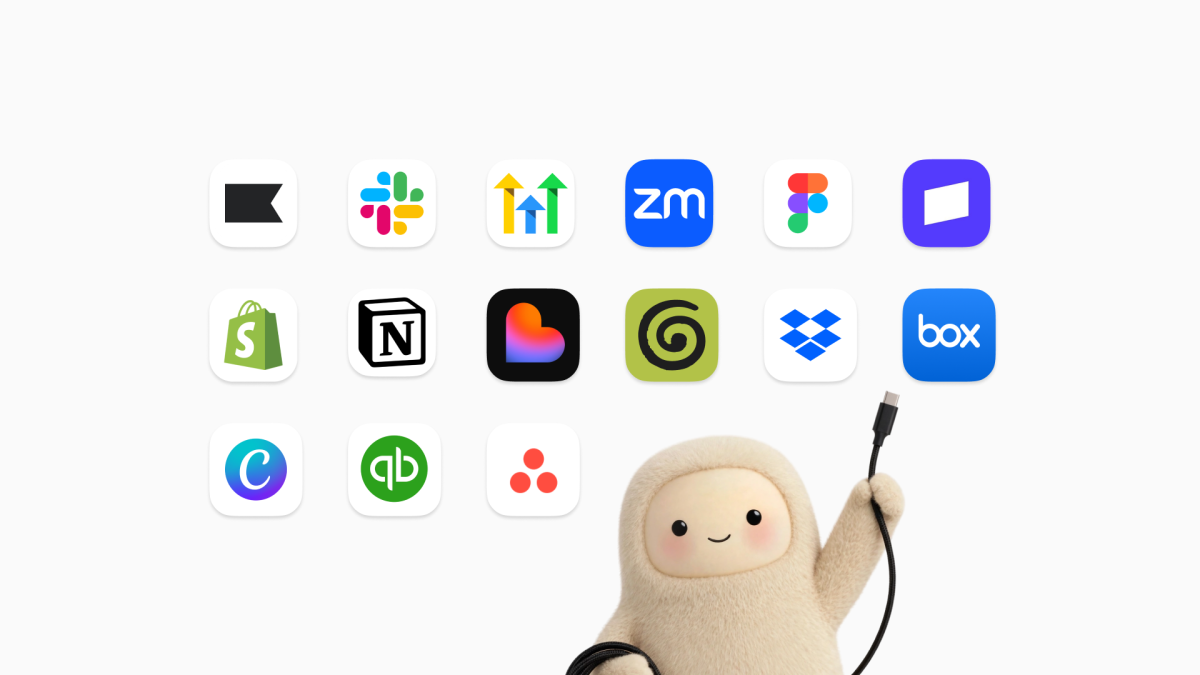
Meta announced on Tuesday that it’s expanding its AI agent Muse to small businesses and adding new integrations including Shopify, Dropbox, Slack, and more. The tech giant says the agent can help owners run their business and find new customers.
By plugging Muse into the software that small business owners are already using to manage sales, operations, and marketing, Meta is betting that an AI agent with context of a company’s whole operation will be more useful than a standalone chatbot, as it continues to compete against rivals like OpenAI and Google.
Muse can also link to Instagram professional account analytics, Facebook Pages, and Meta ad accounts. Meta says the AI agent also knows what a business sells, how a brand sounds, and what customers ask about most.
Additional integrations include Asana, Box, Canva, Figma, Granola, HighLevel, Intuit QuickBooks, Klaviyo, Lovable, Notion, Stripe, and Zoom.
Muse for Small Business is available for free with usage limits. Businesses that want more usage can purchase a subscription plan.

“Small businesses have been growing on our apps for nearly two decades,” Meta wrote in a blog post. “They told us they’re short on hours, not ideas. So we built Muse for Small Business to help get work done with the tools they already use.”
Meta has been focused on expanding its AI tools beyond the consumer and into the enterprise market. The launch of Muse for Small Business comes a day after Meta introduced “Meta Enterprise Platform,” a new initiative aimed at expanding the company’s AI offerings to businesses and corporate customers. The move could help Meta see a return on all the money it’s pouring into AI.
The tech giant hired Chirantan “CJ” Desai, the CEO of database software giant MongoDB, to lead the new initiative.
Meta says it will focus on bringing its full technology stack, including Muse, Meta Business Agent, Muse API, Muse Code, and more, to businesses and developers.
The rollout of Meta Enterprise Platform is built on the momentum of Muse, which launched earlier this month and topped the U.S. and Canada app charts ahead of ChatGPT.
When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.
>
Apple has fixed a security vulnerability in its iOS 26, iPadOS 26 and macOS 26 operating systems that the company says “may have been exploited” by hackers. The tech giant said the now-fixed bug could be used to launch “an extremely sophisticated attack against specific targeted individuals on versions of iOS before iOS 27.”
According to a listing on Apple’s security pages, the bug was found in the main graphics engine that powers the user interface and visuals on iPhones, iPads and Macs.
Meta’s product security team was credited with the discovery.
Details of the bug, officially classed as CVE-2026-86950, were not released, but a device’s graphics engine typically has broad access to the rest of the device’s operating system. A successful exploit could potentially allow a hacker to steal a broad range of personal data from an affected device.
When reached by TechCrunch, spokespeople for Apple and Meta did not provide comment about how the bug was discovered, or how many people had their devices hacked due to this vulnerability, if any. It’s also unclear who may be exploiting the bug, such as government spyware makers or cybercriminals.
While the bug affects Apple’s previous generation of operating systems, it remains in wide usage. Almost four-in-five of Apple’s iPhone owners are still running iOS 26, according to the company’s own statistics. Devices running the latest version, iOS 27, iPadOS 27, and macOS 27, released earlier this month, also received a software update on Tuesday, but are unaffected by the bug under attack.
A separate ‘zero-click’ bug now fixed
News of the security patch comes soon after Apple fixed another critical security bug, known as CVE-2026-86869, which could have allowed hackers to silently steal data from affected iPhones, iPads, or Macs.
Belgian cybersecurity research firm ironPeak published a detailed writeup last week explaining that the bug was a “zero-click” vulnerability that could be invisibly triggered via a maliciously crafted iMessage, without the user’s knowledge. Such bugs require no interaction from the victim, such as clicking a link, and are highly sought-after by surveillance vendors and spyware makers.
Per ironPeak’s post, the bug is capable of bypassing BlastDoor, a security feature that Apple implemented to prevent malicious code, like spyware, from escaping iMessage’s sandbox and hacking the user’s device.
Apple fixed the bug in September with the release of iOS 27, iPadOS 27, and macOS 27, and credited ironPeak’s Niels Hofmans with the discovery, alongside security researchers at Meta who confirmed their findings in a post on X.
It’s not yet known if this bug had been used in cyberattacks before it was fixed.
When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.
>

Avengers: Doomsday Full Cast List: Russos Tease Secret Characters

1 in 100 (GFs) – This Week in Anime

Why Salisbury FC are ‘bigger than many Premier League teams’ in Kuwait
-

 movies4 months ago
Search For Canadian TV Actor Stewart McLean Now Homicide Investigation
-

 Fashion9 years ago
These ’90s fashion trends are making a comeback in 2017
-
Fashion9 years ago
According to Dior Couture, this taboo fashion accessory is back
-
Fashion9 years ago
Model Jocelyn Chew’s Instagram is the best vacation you’ve ever had
-
Fashion9 years ago
Emily Ratajkowski channels back-to-school style
-
Fashion9 years ago
9 Celebrities who have spoken out about being photoshopped
-
 Anime4 months ago
Rurouni Kenshin: Hokkaido Arc Manga Takes 1-Issue Break – News
-

 Anime3 months ago
HIDIVE to Stream English Dubs for The World Is Dancing, The Forsaken Saintess and Her Foodie Roadtrip in Another World, The Dangers in My Heart: The Movie Anime – News