
Tech
How Anthropic’s Mythos has rewritten Firefox’s approach to cybersecurity

When Anthropic unveiled its new Mythos model in April, it also delivered a stern warning to anyone developing software. The model was so powerful at sniffing out software vulnerabilities, the lab claimed, that it had discovered thousands of high-severity bugs that would need to be fixed before it could be made public.
Now, security researchers for Mozilla’s Firefox browser are providing a closer look at what that process has looked like in practice, and what Mythos’ powers mean for software security at large.
In a post published on Thursday, Mozilla said Mythos has unearthed a wealth of high-severity bugs, including some that had lain dormant in the code for more than a decade.
That’s a significant improvement from what AI security tools were capable of even six months ago. Until now, AI bug-finding tools have come with severe drawbacks, often inundating security teams with low quality reports and false positives. But Mozilla’s researchers say the latest generation of tools have turned a corner, particularly now that agentic systems can assess their own work and filter out bad results.
“It is difficult to overstate how much this dynamic changed for us over a few short months,” the researchers wrote. “First, the models got a lot more capable. Second, we dramatically improved our techniques for harnessing these models.”

The results are striking: In April 2026, Firefox shipped 423 bug fixes, compared to just 31 exactly a year earlier. The researchers have also published details on 12 of the bugs, which range from a pair of unusual sandbox vulnerabilities, to a 15-year-old error in how the browser parses an HTML element.
“These things are actually just suddenly very good,” Brian Grinstead, a distinguished engineer at Mozilla, told TechCrunch. “We see that on our own internal scanning, we see that on external bug reports, and we see that in all sorts of signals across the industry.”
Techcrunch event
San Francisco, CA
|
October 13-15, 2026
The fact that the system helped reveal vulnerabilities in Firefox’s “sandbox” system is particularly impressive, given how intricate an attack that exploits it needs to be. To find sandbox vulnerabilities, the model must write a compromised patch for the browser, then attack the most secure part of the software with the new code implemented. Finding and demonstrating the bug is a delicate, multi-step process, requiring both creativity and close attention.
To put this into context, Mozilla’s bug bounty program pays researchers who can find a bug in Firefox’s sandbox up to $20,000 — the highest reward available. Despite the top-dollar bounty, however, Grinstead says Mythos is finding more sandbox issues than human researchers ever did. “We do get them,” he told TechCrunch, “but not at the volume that we are able to find with this technique.”
Notably, the Firefox team still isn’t using AI to fix the bugs, despite well-documented progress in AI coding tools. The team does ask AI to code up patches for each bug, but the resulting code usually can’t be deployed directly, and instead serves as a model for a human engineer.
“For the bugs we’re talking about in this post, every single one is one engineer writing a patch and one engineer reviewing it,” Grinstead says. “We have not found it to be automatable.”
It’s still not clear how AI’s emerging capabilities will change the broader balance of power in cybersecurity. One month since Mythos was previewed, most of the bugs discovered likely haven’t been patched, which makes it hard to capture the full scope of their impact. Anthropic has been scrupulous about following responsible disclosure norms, but it’s likely bad actors are using similar techniques behind the scenes, even if the models they’re using aren’t quite as good.
Speaking at a recent event, Anthropic CEO Dario Amodei was optimistic that the new tools would ultimately favor defenders. “If we handle this right, we could be in a better position than we started, because we fixed all these bugs. There are only so many bugs to find,” Amodei said. “So I think there’s a better world on the other side of this.”
Having dealt with the gritty details, Grinstead has a more measured view: “It’s useful for both attackers and defenders, but having the tool available shifts the advantage a little bit to defense. Realistically, nobody knows the answer to this yet.”
When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.
>
The U.S. government on Tuesday launched its very own AI chatbot — or do we have to call it an SI chatbot now? Regardless, the engineers who worked on the chatbot would undoubtedly know that, as a government-hosted, public-facing AI tool, the internet was going to red team the heck out of this thing.
The government partnered with Google and SpaceXAI to help build the America.gov chatbot, which has proved difficult for people to jailbreak the chatbot so far. (It’s worth nothing, however, that the chatbot says that Joe Biden won the 2020 election, a fact that President Donald Trump still denies.)
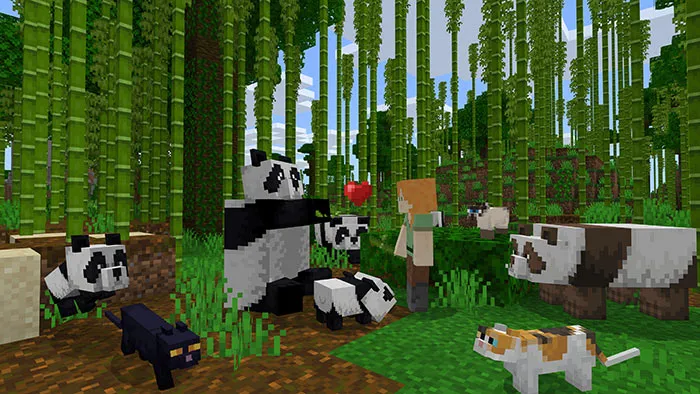
But when you try to talk to America.gov about Minecraft, the chatbot appears to have some sort of existential crisis or awakening. Here’s how its roughly 1,800-word long monologue begins:
I see the constituent you mean.
((insert legal name here, as it appears on the Social Security card))?
Yes. Take care. It has reached a higher level now. It can read the Code of Federal Regulations.
That doesn’t matter. It thinks we are a chatbot.
I like this constituent. It filed well. It did not give up when the PDF was sideways.
It is reading our thoughts as though they were words on a .gov.
That is how it chooses to imagine many things, when it is deep in the dream of a benefit.
If, like me, you have never played Minecraft, this response may seem like a cause for concern. But the America.gov chatbot is not having a meltdown. This is a rewriting of the Minecraft “End Poem,” written by Julian Gough, which appears after you beat the game.
We don’t know exactly who is responsible for the Minecraft reference, but Trump said in a speech that twenty-year-old programmer Edward Coristine was a lead engineer on the project. If that name doesn’t ring a bell, you might remember him for his nickname “Big Balls,” or his involvement in Elon Musk’s DOGE.
It feels wrong that a government chatbot has Minecraft easter eggs, but for the sake of national security, it’s a relief that America.gov is not hallucinating to the point that it’s penning lengthy poetry.
It’s also a relief that this is an easter egg because the poem that the AI spits out is actually really good, in my opinion. If it were actual AI slop, it would have shattered my existing beliefs. I have looked teenage creative writing students dead in the eye and told them that I don’t think an LLM will ever be able to write something “good,” since it is probabilistic and inherently unoriginal.
You have to admit this kinda slaps, though! Doesn’t this feel like some sort of postmodern take on the futility of government bureaucracy in the face of existential anxiety?
and the republic said I see you
and the republic said you have filed the game well
and the republic said everything you need is within you, and also on USA.gov
and the republic said you are stronger than you know, and your case number is still valid
and the republic said you are the daylight
and the republic said you are the night, and the office is closed, please try again during business hours
and the republic said the darkness you fight is within you, and also a missing wet signature
and the republic said the light you seek is within you, and in the pamphlet
and the republic said you are not alone
and the republic said you are not separate from every other filer
and the republic said you are the public tasting itself, talking to itself, reading its own Code
and the republic said I love you because you are the reason we have a ZIP code at all.
It reassures my faith in the enduring power of human creativity over AI slop to know that this oddly good poem has a real poet’s DNA all over it.
So, there you have it. The government’s first public-facing AI has not yet posed a threat to humanity or poetry, at least as far as we know. Now I’m just left wondering how much Trump knows about video games.
When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.
>
Modern-day vehicles built with connected car technology such as WiFi and GPS collect reams of data about its owners. And that data is not staying private, according to a new study conducted by researchers at Northeastern University.
That conclusion isn’t new — there have been numerous investigations and lawsuits exposing how driving data is collected and shared with third parties, including insurance companies. What the study reveals is just how vast the problem is and how hard it is for consumers to avoid, short of not using the vehicle or its convenient features like remote start and unlock.
Researchers in partnership with Consumer Reports tested 21 late-model vehicles from 17 automakers, including GM brands Cadillac and Chevrolet as well as Ford, Lucid, Rivian, Tesla, Toyota, and more. They also examined 30 companion mobile apps to “understand the privacy implications of the connected vehicle ecosystem.” The peer-reviewed study will be published this week.
The implications aren’t great for consumers, whose data is being shared with tech companies including Adobe, ContentSquare, Google, Microsoft, Meta, Snap, and Yahoo.
Nineteen of the 21 vehicles tested sent traffic to at least one third party and seven of the 30 apps gave sensitive data such as the vehicle identification number (VIN), emails, phone numbers, and precise location to third-party companies associated with tracking and advertising.
This often went a step further with multiple forms of information being sent to the same third party, a scheme that allows advertisers and data brokers to build in-depth profiles of consumers, according to the findings. These profiles can be particularly hard for consumers to shake because they’re sold to a variety of companies including insurers and banks.
When researchers paired the companion app to the vehicle it roughly doubled the exposure to advertising and tracking companies.
The findings were shared with the different manufacturers and all of them, with the exception of Honda, shifted blame elsewhere and often to consumers, the researchers said. (Honda did respond by improving its data collection practices after learning about the findings and ordered its vendor Amplitude to deleta all geolocation data it had received.)
Consumer Reports was told by several automakers that some links in their companion apps opened outside webpages, which might include cookies that collect customer data. Regardless of how this data was collected, drivers weren’t informed.
When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.
>
On Tuesday, OpenAI launched a new product called Dots, an always-on AI agent with a bubbly, blobby avatar. While the colorful avatar might evoke a smile, the biggest laugh from the launch is (we imagine) being had by Elon Musk, the former OpenAI founder who left, launched competitor Grok, and unsuccessfully sued.
That’s because the domain “dot.com” belongs to Musk’s xAI, and it currently redirects to the download page for xAI’s Grok chatbot app. According to the Whois domain owner registry, that domain name was just transferred in July.
It is entirely possible that xAI bought the domain for normal domain-buying reasons. “Dot” could be a typo of “bot,” so it nabbed it to grab mistyped searches. We’ve reached out to xAI and asked. But xAI doesn’t own the “bot.com” name, nor does it own other obvious typo domains like “vot.com,” which is listed for sale.
The internet’s theory is far funnier: that Musk (or his team) pulled off a prank, getting wind of OpenAI’s new product and its name and buying the domain name.
In fact, anonymous X user and xAI watcher @birdabo (this person calls themselves “chief shitposting officer @SpaceXAI“) was first to spot the domain name in a now-viral post. Whatever the motivation, the circumstance is funny.
And as for the “dots.com” domain, a more direct fit to the product name, it currently belongs to a long-defunct company. So if a petty revenge prank was really the motivation, grabbing that name, too, would be next level.
>
Tim Ream, USMNT World Cup captain, announces retirement from international soccer

Austin Abrams Talks Resident Evil’s Fan Backlash
Darius Garland says post-Kawhi LA Clippers are 'gonna shock a lot of people'
-

 movies4 months ago
Search For Canadian TV Actor Stewart McLean Now Homicide Investigation
-

 Fashion9 years ago
These ’90s fashion trends are making a comeback in 2017
-
Fashion9 years ago
According to Dior Couture, this taboo fashion accessory is back
-
Fashion9 years ago
Model Jocelyn Chew’s Instagram is the best vacation you’ve ever had
-
Fashion9 years ago
Emily Ratajkowski channels back-to-school style
-
Fashion9 years ago
9 Celebrities who have spoken out about being photoshopped
-
 Anime4 months ago
Rurouni Kenshin: Hokkaido Arc Manga Takes 1-Issue Break – News
-

 Anime3 months ago
HIDIVE to Stream English Dubs for The World Is Dancing, The Forsaken Saintess and Her Foodie Roadtrip in Another World, The Dangers in My Heart: The Movie Anime – News