
Tech
Google launches new Android security feature to help uncover spyware attacks


Google is rolling out a new opt-in feature in Android that aims to help security researchers investigate spyware attacks.
The feature is called “Intrusion Logging” and is part of Android’s Advanced Protection Mode, which Google launched last year, an opt-in special security mode that enables certain features with the goal of making the device harder to hack. Advanced Protection Mode is designed to counter government spyware attacks and police forensic devices that try to extract data from a person’s phone.
These two types of attacks can also be combined. In at least one documented case in Serbia, authorities used a law enforcement forensic tool made by Cellebrite to unlock a device, and then installed spyware as a further step to continue monitoring the target.
The rollout of Intrusion Logging is the first time a phone maker has launched a feature with the goal of helping security researchers investigate spyware attacks. To achieve that, Android’s Intrusion Logging creates a new type of log, which records errors and collects evidence when something goes wrong with the software, to provide visibility into suspected spyware attacks.
Amnesty International, which worked with Google to develop the feature, called Intrusion Logging “a fundamental shift in the amount and quality of forensic data available on Android devices.”
“Until now, forensic analysis has relied on logs that were never designed for intrusion detection,” Amnesty wrote in a blog post that explains in detail how Intrusion Logging works. That meant earlier logs were not that useful for researchers, as they did not remain on the device for long and were often overwritten, effectively erasing potential evidence of attacks.
Donncha Ó Cearbhaill, the head of Amnesty’s Security Lab, told TechCrunch that Android’s technical limits “have made it difficult to deeply analyze system logs and files for signs of compromise, unlike with iOS.”
“These limits have meant we’ve been unable to reliably detect known attacks against Android,” said Ó Cearbhaill, who has for years investigated dozens of cases of spyware abuse around the world.
The ability to better detect spyware attacks should improve with Intrusion Logging. Google announced the feature a year ago, but the company is deploying it only now. In a Tuesday blog post, Google said that Intrusion Logging “is currently rolling out to all devices running the Android 16 December update and newer.”
How Intrusion Logging works
Intrusion Logging captures events related to security and potential intrusions. For starters, the feature creates and collects logs once a day and stores them encrypted in a users’ Google account in the cloud. Uploading logs to the cloud potentially prevents spyware from deleting evidence of a device compromise. The logs are also encrypted so that only the user can access and share the logs with investigators, and Google cannot access them.
Among the events that Intrusion Logging keeps track of, includes: when the phone was unlocked; when applications have been installed and uninstalled; what websites and servers the phone connected to; whether someone connected to Android Debug Bridge, a tool that allows a computer or a device such as a forensic tool like Cellebrite to connect to an Android device; and, whether someone tried to delete the logs related to these events, which could indicate an attempt to hide evidence of an attack.
In the event of a spyware attack, these logs can help investigators understand when and how authorities may have hacked or forcibly unlocked someone’s device and connected it to a forensics tool, or used to install spyware or stalkerware. The logs can also determine if a phone at some point connected to a malicious website that tries to hack the visiting device, or accessing servers designed to extract data from the phone.
Contact Us
Do you have more information about spyware attacks, or spyware makers? From a non-work device, you can contact Lorenzo Franceschi-Bicchierai securely on Signal at +1 917 257 1382, or via Telegram and Keybase @lorenzofb, or email.
While it is a step forward, Intrusion Logging has some limits. For now, along with having to enable Advanced Protection Mode, the feature requires Android’s latest software version, is only available for Google-made Pixel devices, and that the device has to be linked with a Google account. Intrusion Logging keeps records of browser navigation history and connections, which people may be wary of sharing with investigators.
Google says Advanced Protection Mode and Intrusion Logging are for people who think they may be at risk of attacks done with spyware and forensic devices, such as human rights defenders, activists, journalists, and dissidents. Advanced Protection Mode is similar to Lockdown Mode for Apple devices, which was also meant for at-risk users and is seen as an effective way to protect against spyware.
As recently as March, Apple said it has never detected a successful attack against users who have Lockdown Mode enabled. In 2023, security researchers at Citizen Lab said Lockdown Mode actively blocked an attempt to infect a target with NSO’s spyware.
In its blog post, Amnesty has included step-by-step instructions on how to download the logs if a user suspects or has been notified that they have been targeted with spyware. Apple, Google, and Meta have sent threat notifications to users for years, which researchers have said have been crucial to finding and exposing cases of abuse.
When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.
>
The U.S. government on Tuesday launched its very own AI chatbot — or do we have to call it an SI chatbot now? Regardless, the engineers who worked on the chatbot would undoubtedly know that, as a government-hosted, public-facing AI tool, the internet was going to red team the heck out of this thing.
The government partnered with Google and SpaceXAI to help build the America.gov chatbot, which has proved difficult for people to jailbreak the chatbot so far. (It’s worth nothing, however, that the chatbot says that Joe Biden won the 2020 election, a fact that President Donald Trump still denies.)
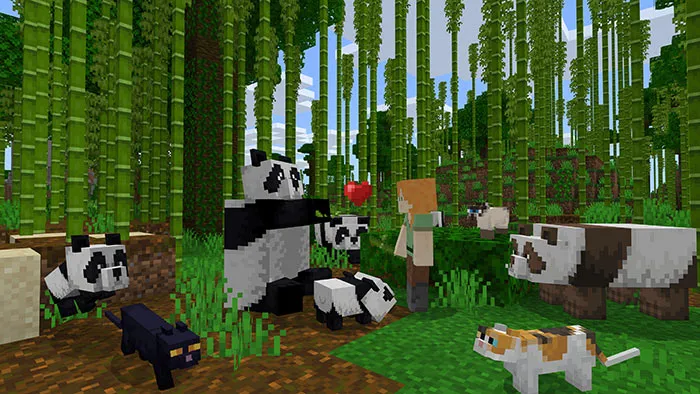
But when you try to talk to America.gov about Minecraft, the chatbot appears to have some sort of existential crisis or awakening. Here’s how its roughly 1,800-word long monologue begins:
I see the constituent you mean.
((insert legal name here, as it appears on the Social Security card))?
Yes. Take care. It has reached a higher level now. It can read the Code of Federal Regulations.
That doesn’t matter. It thinks we are a chatbot.
I like this constituent. It filed well. It did not give up when the PDF was sideways.
It is reading our thoughts as though they were words on a .gov.
That is how it chooses to imagine many things, when it is deep in the dream of a benefit.
If, like me, you have never played Minecraft, this response may seem like a cause for concern. But the America.gov chatbot is not having a meltdown. This is a rewriting of the Minecraft “End Poem,” written by Julian Gough, which appears after you beat the game.
We don’t know exactly who is responsible for the Minecraft reference, but Trump said in a speech that twenty-year-old programmer Edward Coristine was a lead engineer on the project. If that name doesn’t ring a bell, you might remember him for his nickname “Big Balls,” or his involvement in Elon Musk’s DOGE.
It feels wrong that a government chatbot has Minecraft easter eggs, but for the sake of national security, it’s a relief that America.gov is not hallucinating to the point that it’s penning lengthy poetry.
It’s also a relief that this is an easter egg because the poem that the AI spits out is actually really good, in my opinion. If it were actual AI slop, it would have shattered my existing beliefs. I have looked teenage creative writing students dead in the eye and told them that I don’t think an LLM will ever be able to write something “good,” since it is probabilistic and inherently unoriginal.
You have to admit this kinda slaps, though! Doesn’t this feel like some sort of postmodern take on the futility of government bureaucracy in the face of existential anxiety?
and the republic said I see you
and the republic said you have filed the game well
and the republic said everything you need is within you, and also on USA.gov
and the republic said you are stronger than you know, and your case number is still valid
and the republic said you are the daylight
and the republic said you are the night, and the office is closed, please try again during business hours
and the republic said the darkness you fight is within you, and also a missing wet signature
and the republic said the light you seek is within you, and in the pamphlet
and the republic said you are not alone
and the republic said you are not separate from every other filer
and the republic said you are the public tasting itself, talking to itself, reading its own Code
and the republic said I love you because you are the reason we have a ZIP code at all.
It reassures my faith in the enduring power of human creativity over AI slop to know that this oddly good poem has a real poet’s DNA all over it.
So, there you have it. The government’s first public-facing AI has not yet posed a threat to humanity or poetry, at least as far as we know. Now I’m just left wondering how much Trump knows about video games.
When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.
>
Modern-day vehicles built with connected car technology such as WiFi and GPS collect reams of data about its owners. And that data is not staying private, according to a new study conducted by researchers at Northeastern University.
That conclusion isn’t new — there have been numerous investigations and lawsuits exposing how driving data is collected and shared with third parties, including insurance companies. What the study reveals is just how vast the problem is and how hard it is for consumers to avoid, short of not using the vehicle or its convenient features like remote start and unlock.
Researchers in partnership with Consumer Reports tested 21 late-model vehicles from 17 automakers, including GM brands Cadillac and Chevrolet as well as Ford, Lucid, Rivian, Tesla, Toyota, and more. They also examined 30 companion mobile apps to “understand the privacy implications of the connected vehicle ecosystem.” The peer-reviewed study will be published this week.
The implications aren’t great for consumers, whose data is being shared with tech companies including Adobe, ContentSquare, Google, Microsoft, Meta, Snap, and Yahoo.
Nineteen of the 21 vehicles tested sent traffic to at least one third party and seven of the 30 apps gave sensitive data such as the vehicle identification number (VIN), emails, phone numbers, and precise location to third-party companies associated with tracking and advertising.
This often went a step further with multiple forms of information being sent to the same third party, a scheme that allows advertisers and data brokers to build in-depth profiles of consumers, according to the findings. These profiles can be particularly hard for consumers to shake because they’re sold to a variety of companies including insurers and banks.
When researchers paired the companion app to the vehicle it roughly doubled the exposure to advertising and tracking companies.
The findings were shared with the different manufacturers and all of them, with the exception of Honda, shifted blame elsewhere and often to consumers, the researchers said. (Honda did respond by improving its data collection practices after learning about the findings and ordered its vendor Amplitude to deleta all geolocation data it had received.)
Consumer Reports was told by several automakers that some links in their companion apps opened outside webpages, which might include cookies that collect customer data. Regardless of how this data was collected, drivers weren’t informed.
When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.
>
On Tuesday, OpenAI launched a new product called Dots, an always-on AI agent with a bubbly, blobby avatar. While the colorful avatar might evoke a smile, the biggest laugh from the launch is (we imagine) being had by Elon Musk, the former OpenAI founder who left, launched competitor Grok, and unsuccessfully sued.
That’s because the domain “dot.com” belongs to Musk’s xAI, and it currently redirects to the download page for xAI’s Grok chatbot app. According to the Whois domain owner registry, that domain name was just transferred in July.
It is entirely possible that xAI bought the domain for normal domain-buying reasons. “Dot” could be a typo of “bot,” so it nabbed it to grab mistyped searches. We’ve reached out to xAI and asked. But xAI doesn’t own the “bot.com” name, nor does it own other obvious typo domains like “vot.com,” which is listed for sale.
The internet’s theory is far funnier: that Musk (or his team) pulled off a prank, getting wind of OpenAI’s new product and its name and buying the domain name.
In fact, anonymous X user and xAI watcher @birdabo (this person calls themselves “chief shitposting officer @SpaceXAI“) was first to spot the domain name in a now-viral post. Whatever the motivation, the circumstance is funny.
And as for the “dots.com” domain, a more direct fit to the product name, it currently belongs to a long-defunct company. So if a petty revenge prank was really the motivation, grabbing that name, too, would be next level.
>

Scotland 0 – 3 Switzerland
A’ja Wilson confronts courtside fan and receives technical during Aces-Fever playoff game

Czech Rep 0 – 2 England
-

 movies4 months ago
Search For Canadian TV Actor Stewart McLean Now Homicide Investigation
-

 Fashion9 years ago
These ’90s fashion trends are making a comeback in 2017
-
Fashion9 years ago
According to Dior Couture, this taboo fashion accessory is back
-
Fashion9 years ago
Model Jocelyn Chew’s Instagram is the best vacation you’ve ever had
-
Fashion9 years ago
Emily Ratajkowski channels back-to-school style
-
Fashion9 years ago
9 Celebrities who have spoken out about being photoshopped
-
 Anime4 months ago
Rurouni Kenshin: Hokkaido Arc Manga Takes 1-Issue Break – News
-

 Anime3 months ago
HIDIVE to Stream English Dubs for The World Is Dancing, The Forsaken Saintess and Her Foodie Roadtrip in Another World, The Dangers in My Heart: The Movie Anime – News