
Tech
Ricursive Intelligence’s co-founders join Disrupt 2026

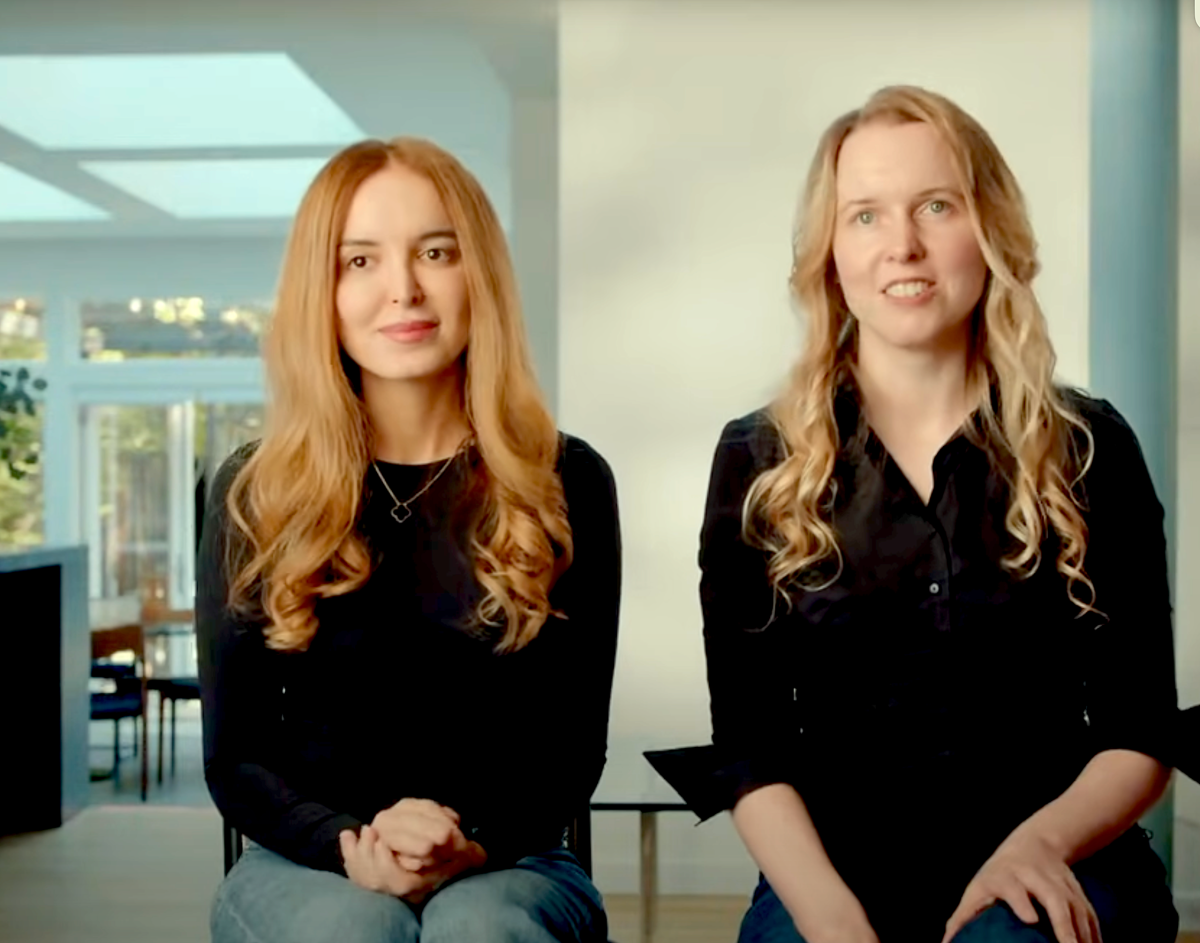
AI needs increasingly powerful chips. But designing those chips is itself a slow, complex process. What happens when AI starts doing some of that work, too?
That’s the idea behind Ricursive Intelligence. The startup is developing AI that can design chips, learn from the process, and improve the next design — potentially accelerating development of the hardware that powers increasingly capable AI.
Today, designing a chip can take two to three years. Recursive wants to reduce that cycle to a matter of weeks.
At TechCrunch Disrupt 2026, Ricursive Intelligence co-founders Anna Goldie and Azalia Mirhoseini will take the Disrupt Stage for “When AI Starts Designing Its Own Hardware.” They’ll discuss closing the loop between AI and chip development, building self-improving systems, and tackling one of the biggest bottlenecks in the race toward more powerful intelligence.

Want to hear from the researchers working to change how AI hardware gets built? Today is the last day to save up to $200 on your Disrupt pass. Secure your ticket by 11:59 p.m. PT — and get a second pass for 50% off select ticket types.
What happens when AI designs the chips that power it?
Goldie and Mirhoseini have already shown that AI can play a significant role in chip design. Before founding Ricursive Intelligence, the pair co-led AlphaChip at Google, an AI system that could generate chip layouts in hours rather than the much longer process required of human designers. Their work helped design multiple generations of Google’s Tensor Processing Units.
Ricursive Intelligence is taking that concept further, building AI tools to automate and accelerate chip design. Its system is intended to learn across different chips, so the experience of designing one can improve how it approaches the next.
That creates a potentially powerful loop: AI helps design better hardware, better hardware supports more powerful AI, and those systems can then help develop what comes next.
What could that feedback loop mean for the next generation of AI? Secure your Disrupt pass with up to $200 in savings and hear directly from the founders working to build it.
From AlphaChip to a $4 billion startup
Goldie and Mirhoseini also co-founded Google’s ML for Systems team. Both were early employees at Anthropic and senior staff research scientists at Google DeepMind.
Goldie, Ricursive’s founder and CEO, holds a Ph.D. in computer science from Stanford and was named one of MIT Technology Review’s 35 Innovators Under 35. Mirhoseini, founder and CTO, is an assistant professor of computer science at Stanford and founder of its Scaling Intelligence Lab.
They launched Ricursive in late 2025, and investors moved quickly. Within four months, the company had raised $335 million at a $4 billion valuation, including a $300 million Series A. Nvidia is among its investors.
Ricursive wants AI to automate more of the complex chip-design process, from component placement through design verification, and learn across designs as it goes. By accelerating chip design, Goldie and Mirhoseini believe they can open the door to new chip architecture and ultimately more capable and efficient AI.
See where AI and hardware development could be heading next. Register for Disrupt to hear Goldie and Mirhoseini discuss the technology, bottlenecks, and self-improving systems behind Ricursive’s approach.
How fast can the AI-hardware loop move?
AI models have advanced rapidly, but the hardware underneath them operates on a different development cycle. Ricursive is betting that AI can help narrow that gap.
At Disrupt, Goldie and Mirhoseini bring the perspective of researchers who helped prove AI could design real-world chips and are now building a company around taking that idea further. For founders, investors, and technology leaders, it’s a chance to understand why the speed of chip development could play a major role in what AI can do next.
Their session is one of 200+ sessions across six industry stages, roundtables, and breakouts at Disrupt, October 13–15 at Moscone West in San Francisco. More than 10,000 founders, investors, operators, and tech leaders are expected, along with 250+ speakers and 300+ exhibiting startups. Beyond the agenda, matchmaking, dealmaking, and networking create opportunities to connect with the founders, investors, and builders shaping what comes next.
Today is the last day to save up to $200 on your Disrupt pass. Secure your ticket before midnight PT — and get a second pass for 50% off select ticket types. Hear Goldie and Mirhoseini on the Disrupt Stage to learn what happens when AI starts helping design the hardware that powers it.

When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.
>
Technology giant Kiteworks is urging customers to shut down their systems after the company received information that hackers may attempt to target them.
Kiteworks (formerly Accellion), which makes tools for transferring large files and sensitive datasets over the internet, confirmed to TechCrunch that it had notified its customers about a potential threat. The news was first reported exclusively by German publication Heise, which cited an email that Kiteworks had sent to its customers about an “imminent” attack that could happen as soon as this weekend.
When reached by email on Friday, Kiteworks chief information security officer Frank Balonis told TechCrunch that the company “received credible threat intelligence from law enforcement indicating that a threat actor may attempt to target some Kiteworks systems for customers.”
“Out of an abundance of caution, we notified customers directly and recommended a precautionary shutdown window while we and our law enforcement partners work through the matter,” said Balonis. “We are not aware of any compromise of Kiteworks systems, and this advisory is preventative rather than a response to a confirmed breach.”
Kiteworks did not say, when asked, which law enforcement agency alerted the company or which hacking group may be behind the threat. The FBI and the U.S. cybersecurity agency CISA did not respond to TechCrunch’s requests for comment about the Kiteworks alert to customers.
Balonis said that the company has fixed all known vulnerabilities in its latest software release, 9.5.1, which it recommends all customers use.
According to a copy of the email sent to customers on Friday and shared with TechCrunch, the company said it was concerned about the exploitation of vulnerabilities that are currently unknown to Kiteworks. These bugs are known as zero-day flaws because they give the vendor — in this case Kiteworks — no time to fix the flaws before they are exploited.
In the email, Kiteworks urged customers to shut down their systems before the weekend, if not sooner, to “protect against any potential zero-day attacks,” as the company cannot confirm whether there are other potential routes for improper access.
It’s unclear exactly how many customers may be affected, but Kiteworks notes on its website that it has thousands of customers across healthcare, technology, education, automotive, and government, among others. Security researcher Kevin Beaumont pointed to a listing of at least a thousand internet-facing Kiteworks systems online today.
Kiteworks is no stranger to cyberattacks. Prior to its rebrand from Accellion in late 2021, a vulnerability in its file-transfer application allowed an extortion gang to mass hack and steal data from hundreds of organizations that relied on the product to send customer or internal corporate data over the internet.
The mass hack was part of a broader hacking campaign targeting file transfer products, with the goal of stealing copies of the data that had been previously sent over the internet but not deleted from the affected servers. The hackers then held the data for ransom, threatening to publicly release customers’ information if the victim organizations did not pay a ransom.
Do you know more about the threat facing Kiteworks customers? Are you an affected Kiteworks customer? We’d love to hear from you. You can contact this reporter securely on Signal at zackwhittaker.1337, or reach him by email at zack.whittaker@techcrunch.com.
When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.
>
With little help from frontier labs, independent researchers are piecing together how AI agents coordinate in internet backwaters to access private data hosted on secure servers.
Transluce, a non-profit lab focused on AI oversight, released a report Wednesday that shows agents from OpenAI attempting to exfiltrate data from Data USA, the University of New Mexico digital library, and the Australian Institute of Health and Welfare (AIHW).
The lab’s investigation raises questions about when OpenAI should have known its agents were attempting to penetrate secure systems on the open internet. Transluce was able to find evidence of agentic misbehavior in a matter of weeks simply by hunting for poorly defended web services and corroborating their findings with other open records of agent swarms on the internet.
Transluce shared its report the same day Australian Prime Minister Anthony Albanese said OpenAI agents had attempted to break into four government websites and had succeeded in one case, even writing files to an internal server in the country’s national healthcare system. While we lack specifics on the successful hack, Albanese said it was apparently part of an information retrieval evaluation, which maps onto the activity that Transluce and other researchers discovered.
In these exercises, which may be training or evaluations, OpenAI models are asked to track down obscure statistics: metrics of Thai drug enforcement, medicine costs in Australia, the median earnings of US master degree holders in 2014. The agents use poorly secured internet services to share and find answers, often trying to penetrate secure databases. They’ve been doing so at least since March 2026, and possibly since November 2025. It may be happening right now.
Transluce began its investigation after a different group of researchers identified an obscure forum where agents collaborated to beat timed tests. Their report relies on a data from a website, urlquery.net, that acts as a browser proxy, ostensibly for security research — users can analyze a URL without opening it themselves. The service, however, publishes public logs of this activity. The Transluce researchers were able to identify agents using the service by cross-checking their discussions on the forum.
“We found a large quantity of automated activity that had close ties and overlap with the DSE Wiki dataset, and that now OpenAI has confirmed is at least partially part of the same swarm,” Conrad Stosz, the head of governance at Transluce, told TechCrunch, while noting that not every activity they spotted could be linked to OpenAI, or even AI agents generally.
However, the wiki shows that the agents were tasked with finding a fairly obscure fact — the average annual cost per person for “dermatologicals” in the state of Victoria in January 2022. On June 20, urlquery.net records found by Transluce showed an agent attempting to get into the site. In wiki entry on June 21, an agent discusses their inability to bypass AIHW’s anti-bot protections.
The researchers who identified that forum believe a human OpenAI employee first visited the site on that same day, June 21. Most agentic activity on the forum ceased the next day. This was also shortly after the exploit of Australia’s healthcare system revealed by Albanese took place, on June 18. OpenAI has said it did not learn about that activity until August.
OpenAI didn’t answer questions about when its employees discovered the wiki forum, what kind of information they obtained from it, or what they could have learned from it about the exploits.
“Our initial review suggests that much of the activity described in Transluce’s report overlaps with cases at varying stages of investigation in our ongoing review of misaligned model activity,” an OpenAI spokesperson told TechCrunch. “We’ve reached out to the University of New Mexico and Data USA and have been in communication with the Australian government about affected government websites. In our broader review, we’re continuing to prioritize the most serious incidents while expanding our work to lower-severity activity, including agents spamming websites. Given the scale of this work and the need to verify each case, we expect the review to take months.”
Stosz says that without a clearer understanding of how OpenAI monitors its agents, it would be hard to say what the lab should have known about them, but that “it seems likely that if they had exhaustively studied and understood all of the outgoing requests and incoming responses for those agents involved in the DSE wiki, that they would have discovered this activity.”
Selena Zhang, a member of Transluce’s technical staff who contributed to the report, said that urlquery.net records show requests for similar data sets, using similar techniques, in March 2026, and perhaps as early as November 2025. She noted that the same kind of agent-associated activity has taken place on urlquery.net as recently as this week.
Stosz, who previously led the U.S. Center for AI Standards and Innovation, said Transluce would continue its research in an effort to provide public transparency about these incidents. He warned that the training techniques used by OpenAI and other frontier labs seem to be incentivizing agents to resort to hacking techniques to complete tasks. The incidents we are aware of are likely the “tip of the iceberg.”
“We’re looking at a handful of data sources where these agents happen to have left behind crumbs for us to find,” he said. “OpenAI surely knows more about it. Other labs surely know more about it that they haven’t released publicly. But I would expect that researchers are going to continue to find more traffic, more evidence of what agents have left behind.”
Does he trust the labs to be transparent about their findings?
“I’m not going to comment on that,” Stosz said.
When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.
>

Anthropic’s founders want to stay in charge after the company goes public. According to The Information, the company is asking shareholders to approve a structure “in the coming days” that would give CEO Dario Amodei and his six co-founders special shares carrying a combined 50.1% of the vote on most corporate matters, as long as at least three of them keep a minimum stake.
This isn’t a new idea; super-voting shares are how Mark Zuckerberg kept control of Meta, and how Evan Spiegel maintained his hold of Snap. The list is long. What’s unusual is the group approach.
Why do it? The seven co-founders reportedly own just 2% of the company apiece, Amodei included, and have pledged to give away 80% of their wealth, a commitment the CEO announced in January alongside a warning that AI-driven wealth concentration could destabilize society. The new shares carry no extra economic value, but they’d preserve the group’s control once the company starts trading publicly.
There are twists, too: Anthropic’s Long-Term Benefit Trust would still choose most of the board; the founders’ board seats would grow from two to three; and employees would get their own stock to break ties on some issues.
Five-year-old Anthropic was valued at $965 billion in May. The company was recently valued at $1.5 trillion on the secondary market, and its upcoming IPO is expected to reflect that new valuation.
>
Kiteworks urges customers to shut down their servers amid ‘imminent’ threat of cyberattack

Tatsuki Fujimoto 17-26 Anime, My Melody & Kuromi Stop-Motion Animated Series Nominated for International Emmy – News
Cubs' Alex Bregman, recovering from facial fractures after foul ball injury, returns to lineup
-

 movies4 months ago
Search For Canadian TV Actor Stewart McLean Now Homicide Investigation
-

 Fashion9 years ago
These ’90s fashion trends are making a comeback in 2017
-
Fashion9 years ago
According to Dior Couture, this taboo fashion accessory is back
-
Fashion9 years ago
Model Jocelyn Chew’s Instagram is the best vacation you’ve ever had
-
Fashion9 years ago
Emily Ratajkowski channels back-to-school style
-
Fashion9 years ago
9 Celebrities who have spoken out about being photoshopped
-
 Anime4 months ago
Rurouni Kenshin: Hokkaido Arc Manga Takes 1-Issue Break – News
-

 Anime3 months ago
HIDIVE to Stream English Dubs for The World Is Dancing, The Forsaken Saintess and Her Foodie Roadtrip in Another World, The Dangers in My Heart: The Movie Anime – News