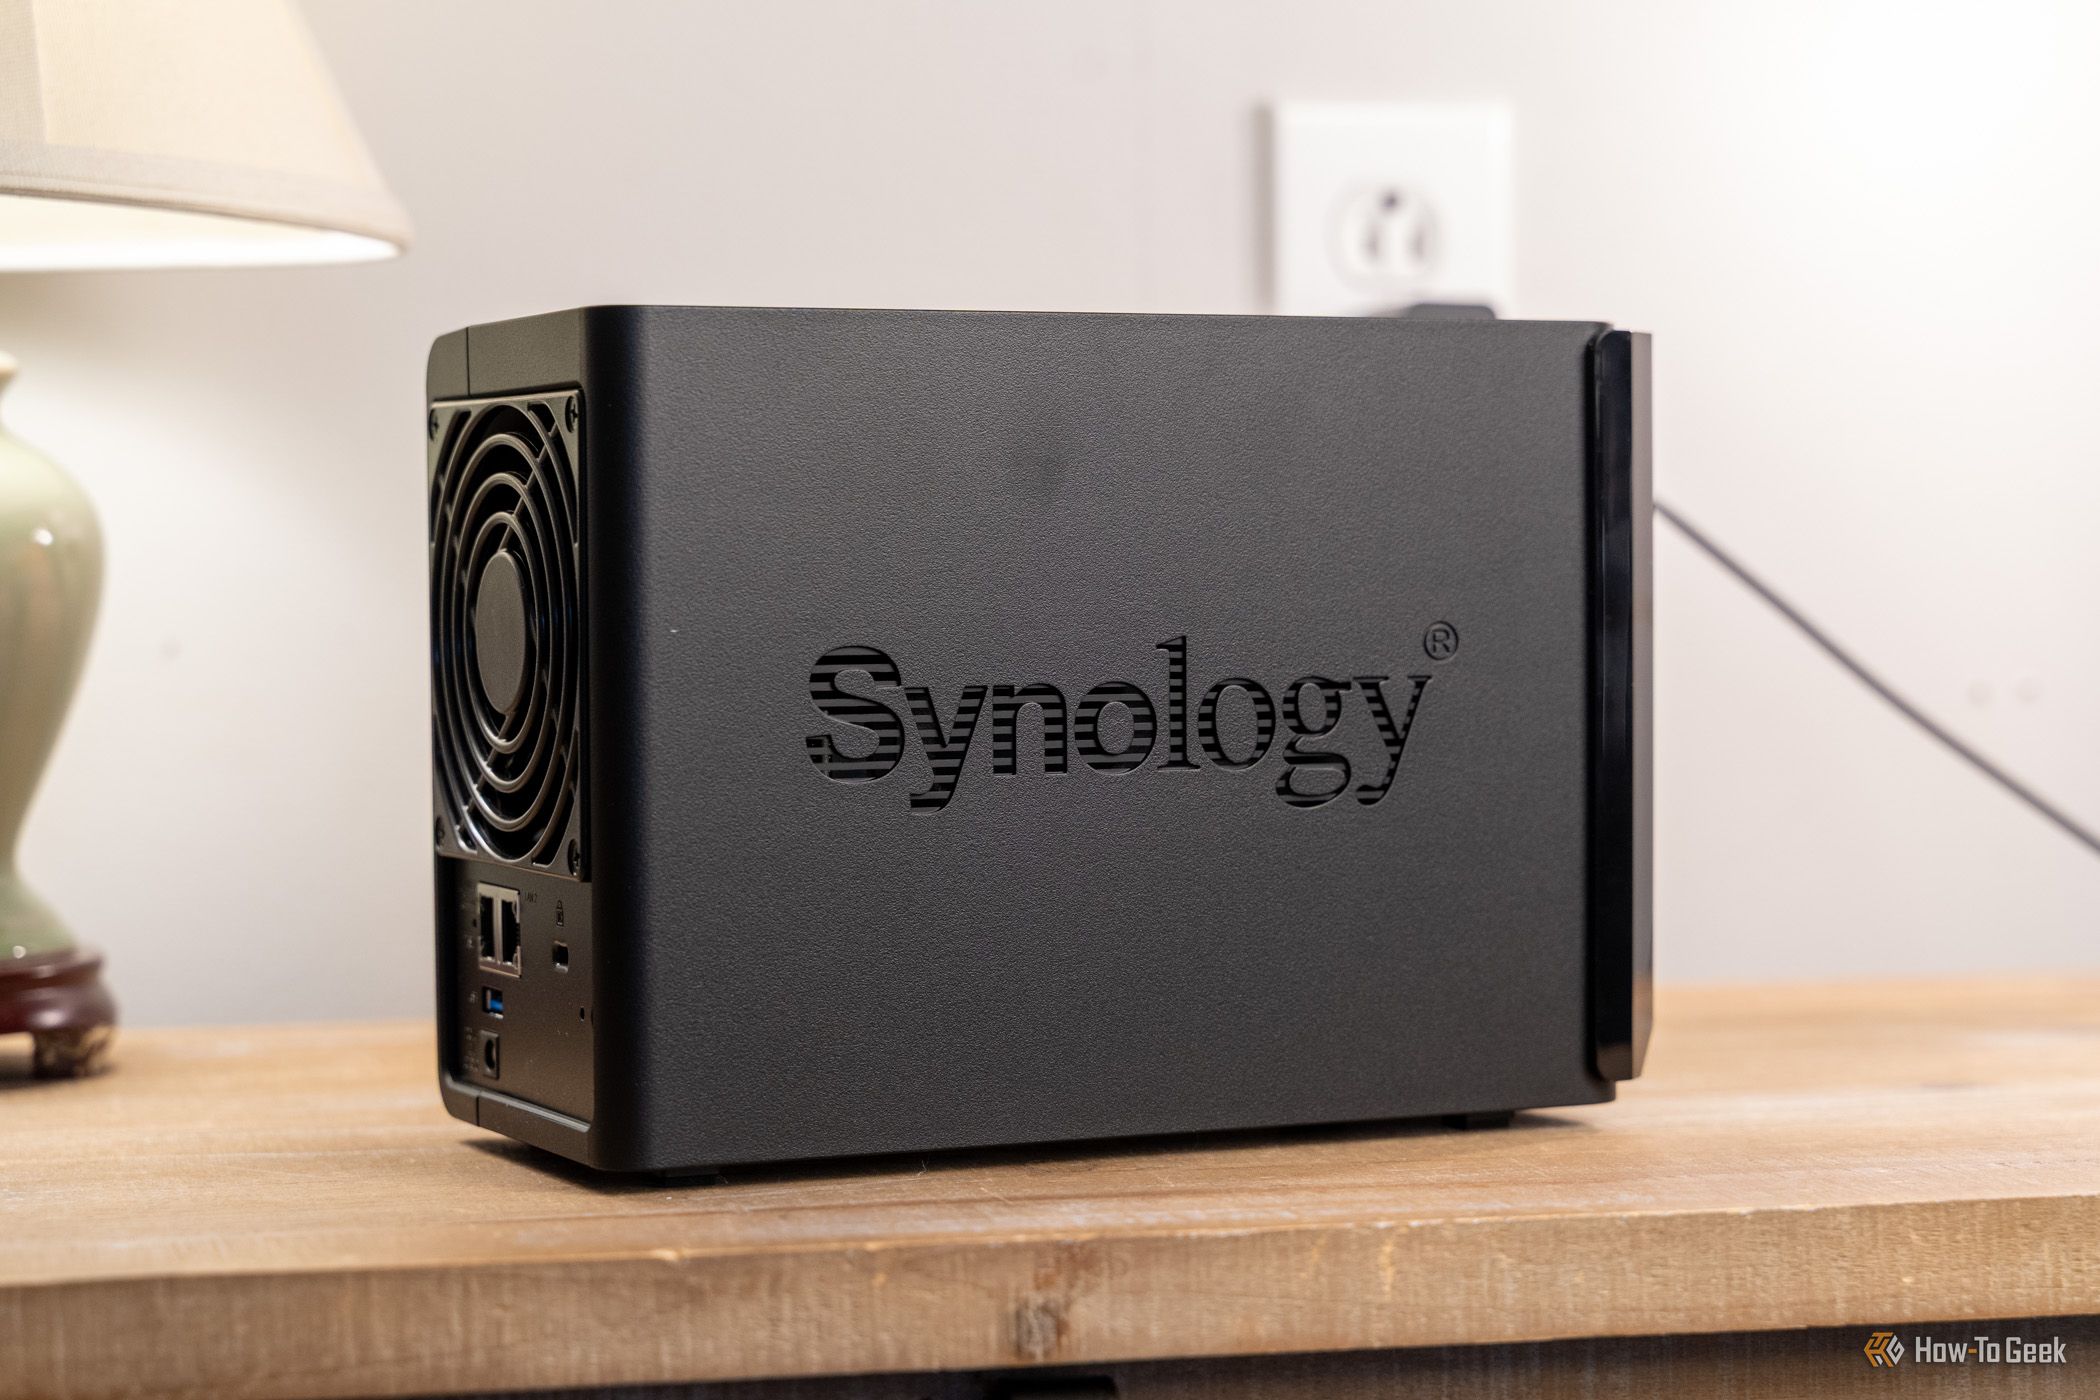
If you own a Synology NAS, stop what you’re doing and check your updates. Synology has rushed out more security fixes for the PHP2Shell vulnerabilities (CVE-2026-109618 and CVE-2026-109619) as attackers actively exploit the flaws — and a separate ransomware campaign is targeting outdated NAS systems, encrypting users’ data and holding it for ransom.
The PHP developers released emergency security patches on October 21, and Synology confirmed that several of its NAS packages were affected. The US cybersecurity agency CISA has since added the flaws to its Known Exploited Vulnerabilities catalog.
Is Your Synology NAS Vulnerable?
Synology’s Product Security Incident Response Team says the flaws affect only some PHP-dependent packages, not every NAS running DSM. The affected packages are: Calendar, IDrive, Joomla, KodExplorer, MailStation, MediaWiki, phpMyAdmin, vtigerCRM, Web Station, and WordPress. If you run any of these on your NAS, you’re in the danger zone.
Note that DSM’s internal PHP component — used for system operations — has no externally accessible modules, so it isn’t exposed to attackers. Still, scan results and compliance status matter, and Synology is patching it in a future DSM update.
How to Patch Your Synology NAS Now
Synology has released PHP security updates for DSM 7.4 and 7.3, plus the older end-of-life versions DSM 7.2, 7.1, 7.0, and 6.2 — a remarkably wide rollout for versions that are no longer supported. Here’s what to do:
1. Open Package Center on your NAS and update PHP for the affected packages. 2. Dependent packages should restart automatically after the update — except MailStation, which you must update manually. 3. On DSM versions older than 6.2, temporarily disable the affected packages to reduce exposure, then upgrade to a supported DSM release.
Bottom line: this is a “patch now” situation, especially for older systems. Hackers are already scanning for unpatched NAS boxes — don’t let yours be one of them.
Image credits: How-To Geek
Source: How-To Geek — read the full story there.